If you are searching for how to turn magic_quotes_gpc on or off, the short answer is that you no longer can. The setting was removed from PHP more than ten years ago, so on any supported PHP version it is simply gone. This guide explains what it did, why the old .htaccess and ini_set() tricks fail, and how to fix an old script that depended on it.
magic_quotes_gpc was deprecated in PHP 5.3 and removed in PHP 5.4, and the helper function get_magic_quotes_gpc() was removed in PHP 8.0. It cannot be enabled on any modern PHP version, and a php_flag line in .htaccess causes a 500 error on our servers. Remove the old magic-quotes checks from your code, use prepared statements for the database and htmlspecialchars() for output.
1. What magic_quotes_gpc did
When magic_quotes_gpc was on, PHP automatically added a backslash before every single quote, double quote, backslash and NUL byte in GET, POST and cookie data (the "gpc"). A name like O'Reilly arrived in your script as O\'Reilly.
It was meant to make careless SQL queries safer, but caused more problems than it solved:
- It escaped for one case only (a quoted MySQL string) and was wrong for HTML, email or files, and it did not reliably stop SQL injection.
- Code had to guess whether the setting was on, so scripts filled up with
stripslashes()calls, and data often ended up escaped twice, with stray backslashes saved in the database.
2. Which PHP versions still have it
| PHP version | magic_quotes_gpc | get_magic_quotes_gpc() |
|---|---|---|
| 5.2 and older | Available, often on by default | Works |
| 5.3 | Deprecated, still works | Works |
| 5.4 to 7.3 | Removed, always off | Always returns false |
| 7.4 | Removed | Deprecated, returns false |
| 8.0 and newer | Removed | Removed: calling it is a fatal error |
So on every PHP version that still receives security fixes, magic quotes are off and there is nothing to disable. If your old script shows Call to undefined function get_magic_quotes_gpc(), it is running on PHP 8 and needs the small fix in section 4.
3. Why the old instructions no longer work
Older guides, including an earlier version of this article, suggested one of these:
php_flag magic_quotes_gpc offini_set('magic_quotes_gpc', '0');Neither works today:
php_flagandphp_valuein.htaccessonly work when PHP runs as an Apache module. None of our shared servers run PHP that way, so the line gives a 500 Internal Server Error. If you added it, remove it. See Troubleshooting 500 Internal Server Error.ini_set()could not change this setting even in PHP 5, because the request data has already been processed by the time your script runs. On PHP 5.4 and newer the setting does not exist at all.
Some old forums suggest running addslashes() over every $_POST value at the top of the script to imitate magic quotes. This brings back all of the old problems and still does not make your queries safe. Fix the queries instead, as shown in section 5.
4. Fixing an old script that relied on magic quotes
Most legacy code contains a pattern like this:
if (get_magic_quotes_gpc()) {
    $name = stripslashes($_POST['name']);
} else {
    $name = $_POST['name'];
}
On modern PHP, replace it with the plain value:
$name = $_POST['name'] ?? '';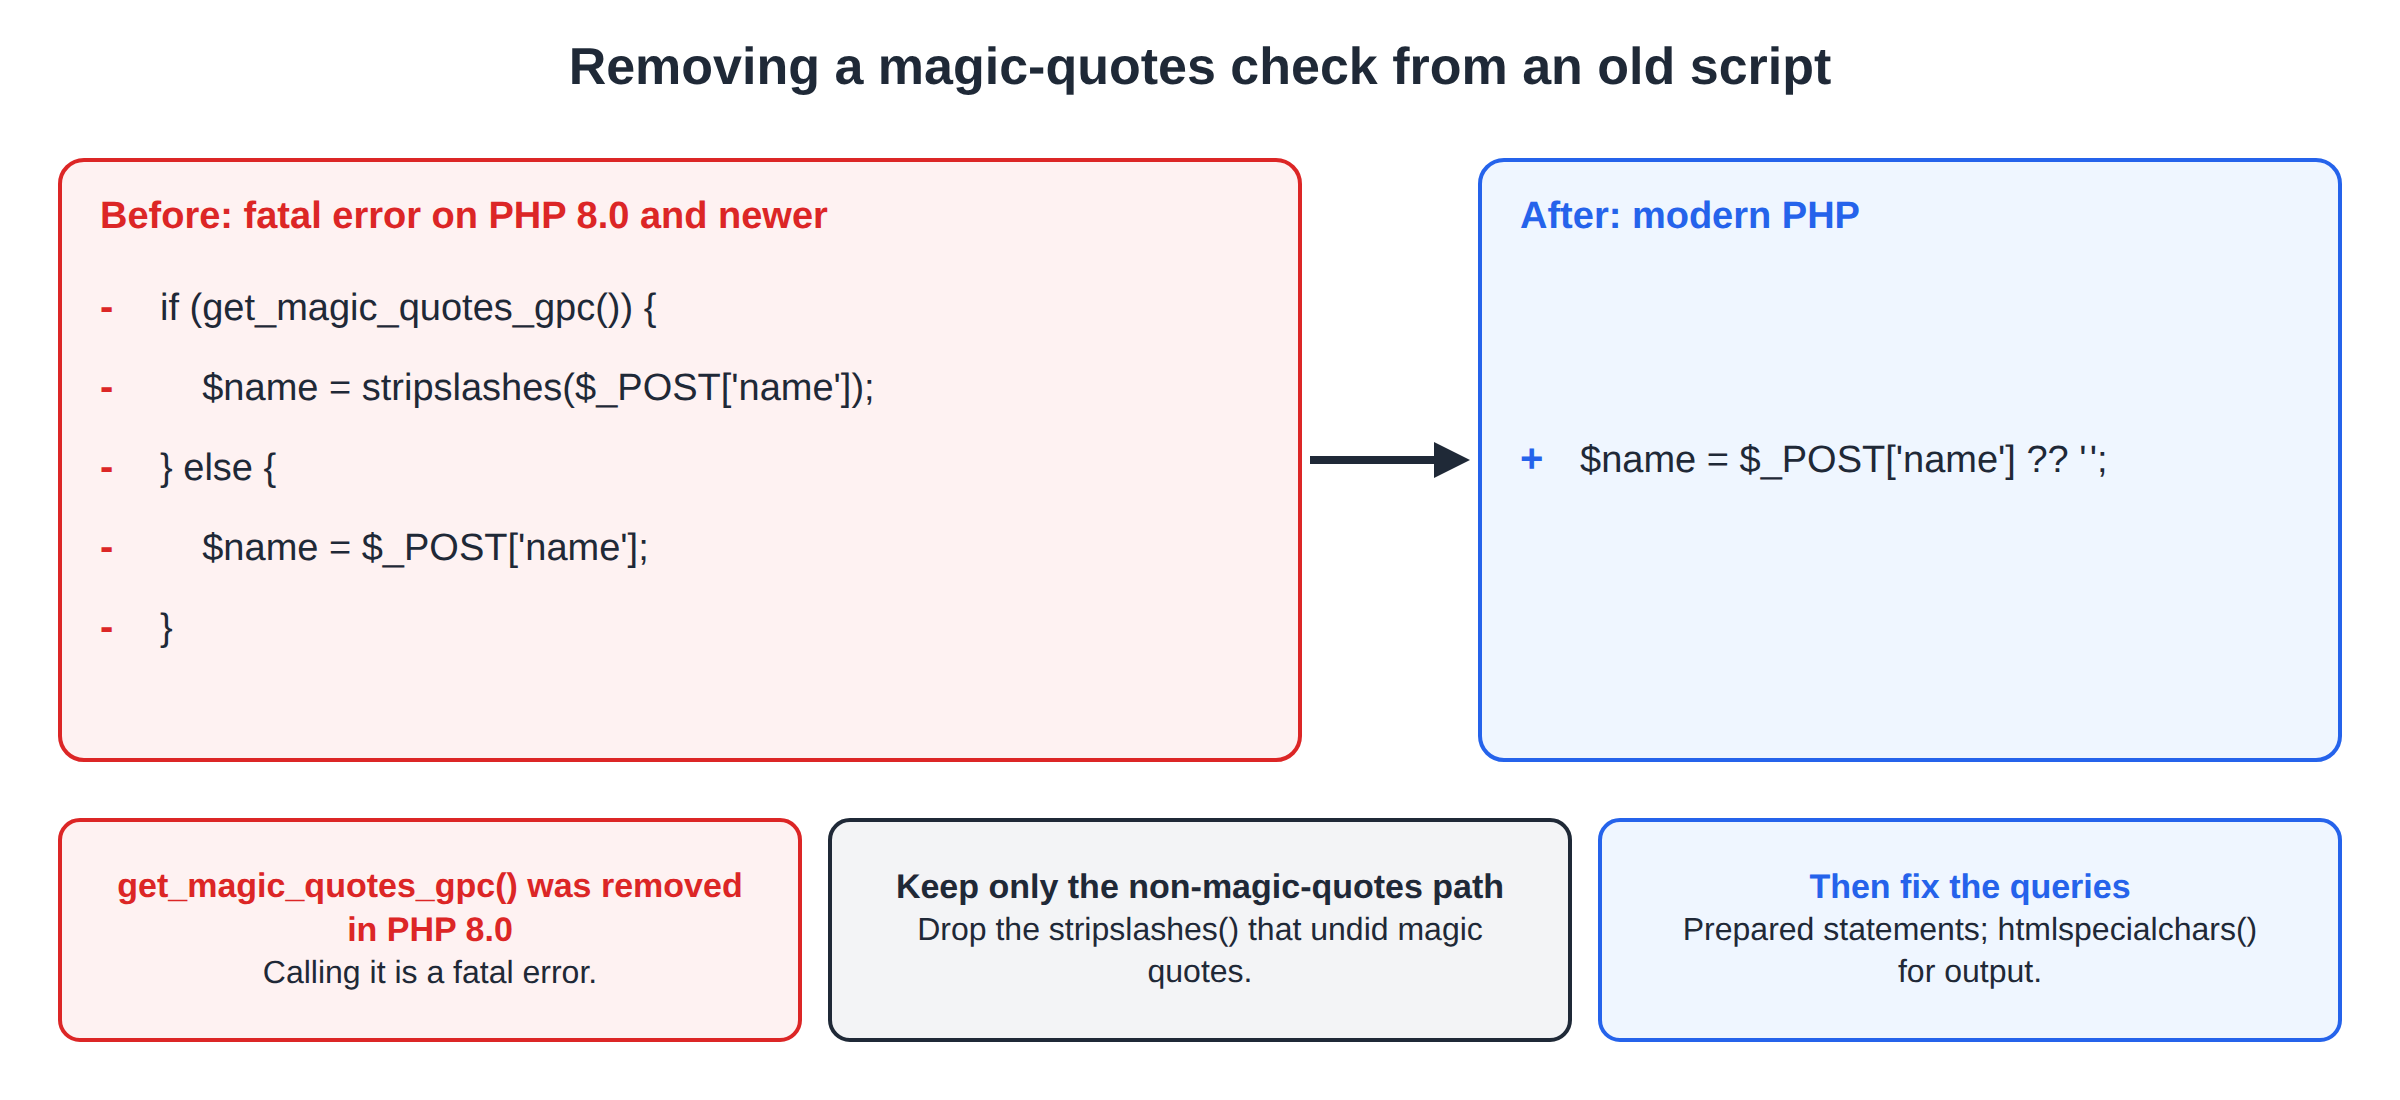
- Take a backup.Download a copy of the site files and export the database before you change anything.
- Search the code.Look for
get_magic_quotes_gpc,get_magic_quotes_runtime,set_magic_quotes_runtimeandstripslashes. The first three can be deleted with the branch they control; keep only the non-magic-quotes path. - Check each stripslashes() call.If it only undid magic quotes, remove it, or it will strip real backslashes that users typed.
- Fix the queries.Code written for magic quotes usually builds SQL by joining strings, and often uses the old
mysql_*functions, which were removed in PHP 7. Move to PDO or MySQLi with prepared statements. - Clean stored data if needed.If records show text such as
O\'Reilly, the old code saved escaped values. Clean them with a careful, tested update on a copy of the database first. - Test on the PHP version you will run.Switch the site to a current PHP version in your control panel and test every form.
5. What to use instead
The modern rule is simple: keep input as it arrives, and escape it at the moment you use it, for the place you use it.
Databases: prepared statements. The value is sent separately from the SQL, so quotes in it cannot change the query:
$pdo = new PDO('mysql:host=localhost;dbname=mydb;charset=utf8mb4', 'dbuser', 'dbpass', [
    PDO::ATTR_ERRMODE => PDO::ERRMODE_EXCEPTION,
]);

$stmt = $pdo->prepare('INSERT INTO customers (name, email) VALUES (?, ?)');
$stmt->execute([$_POST['name'] ?? '', $_POST['email'] ?? '']);
HTML output: htmlspecialchars(). Escape anything a visitor supplied before you print it:
echo htmlspecialchars($name, ENT_QUOTES | ENT_SUBSTITUTE, 'UTF-8');Validation. Check that each value is the type and length you expect, for example with filter_var() for email addresses.
For full examples, read Preventing SQL injection in PHP and Node.js and Preventing XSS in PHP and Node.js.
6. Should you run an old PHP version instead?
Our cPanel servers still have legacy PHP 5.x builds installed for compatibility (measured on our servers, 20 September 2026). That does not make them a good home for a live website. Every PHP 5 release has been without security fixes since the end of 2018, current WordPress and most modern applications will not run on them, and a script that needs magic quotes usually has other security problems too.
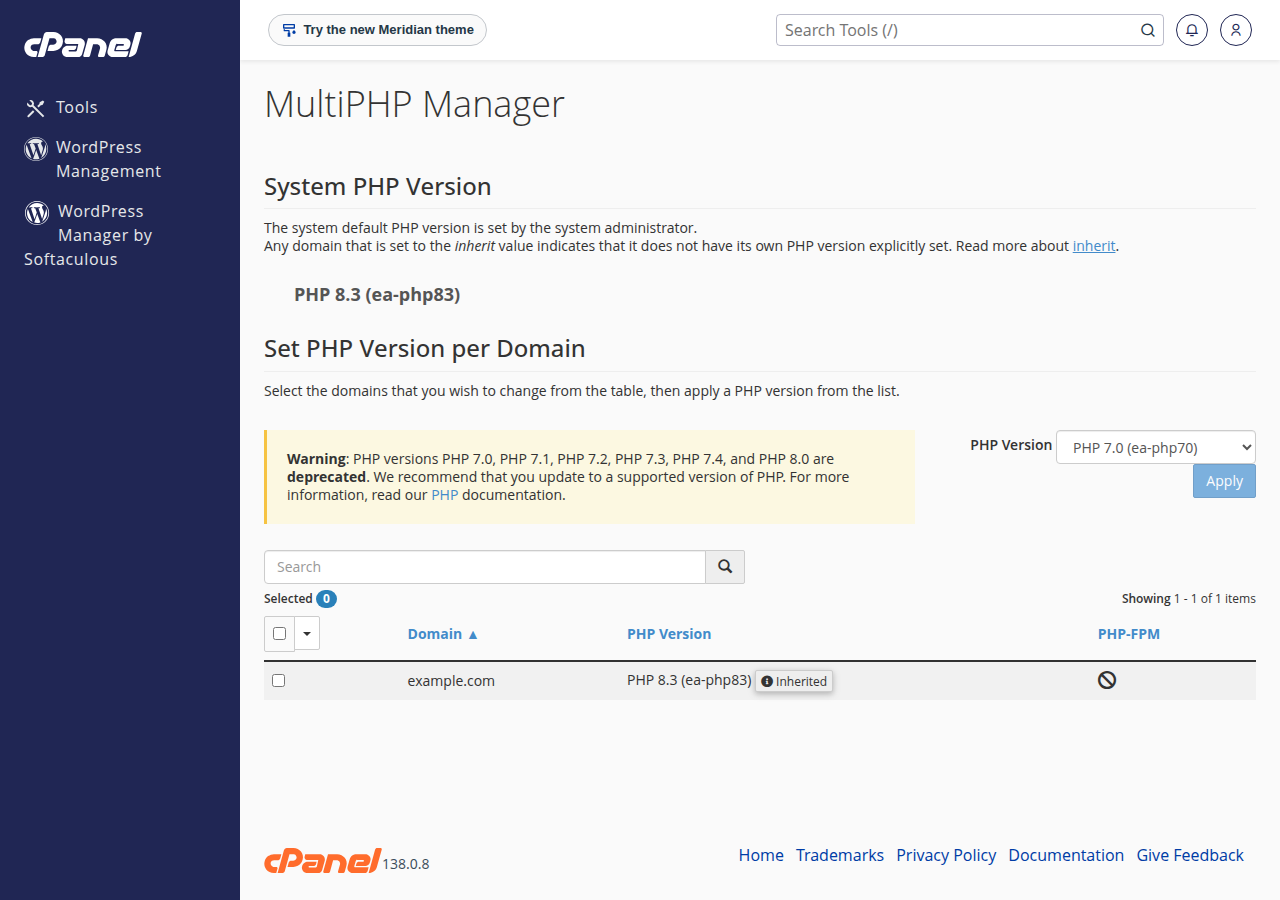
Treat an old PHP version as a short bridge while you fix the code, never as a permanent setting. Understanding PHP version compatibility explains how to test an upgrade, and How to change your PHP version shows where the setting is in each control panel.
7. Where Domain India fits
Our cPanel and DirectAdmin shared hosting plans let you choose the PHP version for each account, and our shared plans offer jailed SSH on request (off by default; ask support to enable it), with Git available inside it. Note that phpinfo() is disabled on our cPanel servers, so check your PHP version in the control panel instead.
- 25 GB NVMe SSD Storage
- 50 GB Monthly Bandwidth
- 1 Website
- 10 Email Accounts
If an old application breaks after a PHP change, open a support ticket with the page address and the exact error message, and our team can help you find the cause.
How do I enable magic_quotes_gpc in PHP?
You cannot on any current PHP version. magic_quotes_gpc was deprecated in PHP 5.3 and removed in PHP 5.4, so the setting does not exist in PHP 5.4, 7 or 8. Update the script to use prepared statements and output escaping instead.
What does "Call to undefined function get_magic_quotes_gpc()" mean?
Your script is running on PHP 8.0 or newer, where get_magic_quotes_gpc() was removed. Delete the check and keep only the code path that runs when magic quotes are off, usually the one without stripslashes().
Why does php_flag magic_quotes_gpc in .htaccess give a 500 error?
php_flag and php_value lines only work when PHP runs as an Apache module. Our shared servers run PHP differently, so Apache rejects the line with a 500 Internal Server Error. Remove the line from .htaccess.
Can I use ini_set to change magic_quotes_gpc?
No. Even in PHP 5, ini_set could not change it, because request data is processed before your script runs. In PHP 5.4 and newer the setting does not exist.
What replaced magic quotes for SQL safety?
Prepared statements with PDO or MySQLi. They send values separately from the SQL, so quotes in user input cannot change the query. For output to a web page, use htmlspecialchars().
Ready to move an old script to modern PHP? Compare cPanel hosting, DirectAdmin hosting and Webuzo hosting, read How to change your PHP version, or open a support ticket if a legacy application stops working.
Pick the PHP version for your account, test your code over SSH, and move legacy scripts to a supported release at your own pace.
See hosting plans